
Microsoft warning about malware concealment 🚨
Microsoft warning about malware concealment 🚨
Context
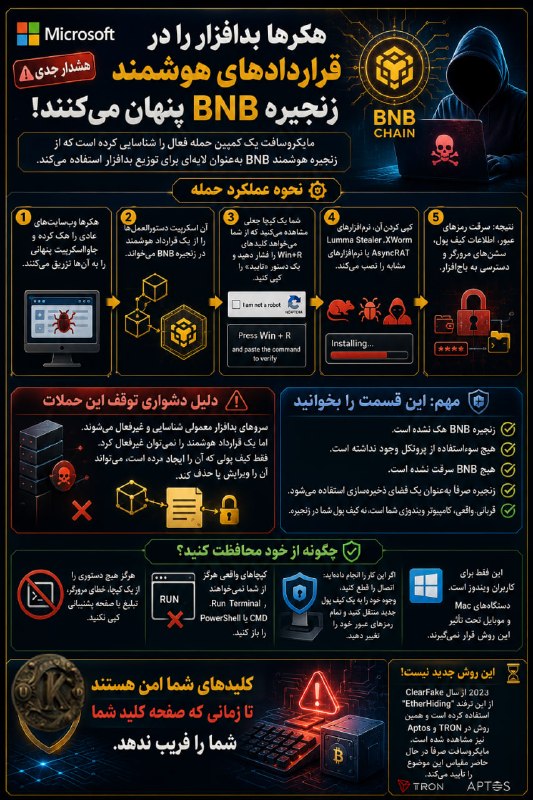
💡 Hackers are using the BNB chain to distribute malware by injecting scripts into websites
🔥 This method, known as EtherHiding, records malicious commands in smart contracts
Focus
🧐 Displaying fake CAPTCHAs and tricking users into executing dangerous commands is the main vector of infiltration
💡 Malware such as RedLine Stealer steals passwords and wallet information
🔥 The BNB chain has not been hacked and is only used as storage space for malicious tools
Consequences
💡 Windows operating systems are the most vulnerable to this attack
🧐 The inability to disable smart contracts makes countering hackers more difficult
Conclusion
🧐 Vigilance against fake commands and avoiding their execution is the most important way to secure oneself 🛡
#Microsoft #Security #Malware #BNB_Chain
Context
💡 Hackers are using the BNB chain to distribute malware by injecting scripts into websites
🔥 This method, known as EtherHiding, records malicious commands in smart contracts
Focus
🧐 Displaying fake CAPTCHAs and tricking users into executing dangerous commands is the main vector of infiltration
💡 Malware such as RedLine Stealer steals passwords and wallet information
🔥 The BNB chain has not been hacked and is only used as storage space for malicious tools
Consequences
💡 Windows operating systems are the most vulnerable to this attack
🧐 The inability to disable smart contracts makes countering hackers more difficult
Conclusion
🧐 Vigilance against fake commands and avoiding their execution is the most important way to secure oneself 🛡
#Microsoft #Security #Malware #BNB_Chain
Persian original · View this post on Telegram ↗ · Open in the archive · 💬 Discuss in the Coin_Kurd Telegram group · Educational, not financial advice.